Incident de sécurité ? Suspicion de compromission ? 09 71 18 27 69csirt@synacktiv.com

Publications

UFC 666 : Frontkick vs Rikugan

13/10/2026
Outils
Dans le coin droit : gratuit, open source, fort de 678 étoiles sur GitHub, champion incontesté de l'agentique sous IDA et prétendant sérieux sur Binary Ninja, voici Rikugan ! Face à lui, encore méconnu mais bien décidé à prendre la relève de son cousin Sidekick, voici Frontkick, un agent spécialisé pour Binary Ninja. Qui du ToolAgent ou du CodeAct l'emportera ? Que le combat commence !

Dites bonjour à Pike!

23/04/2026
Développement
Outils
Système
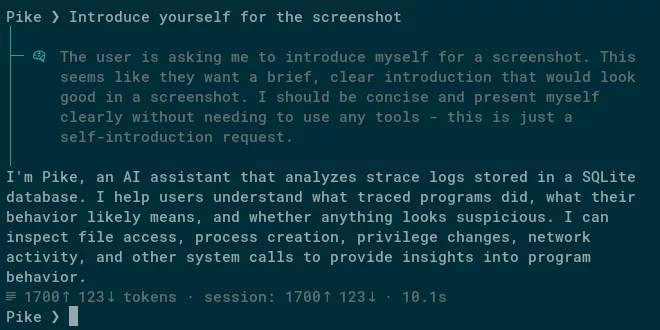
Dans cet article, nous allons présenter Pike, un agent LLM expérimental capable de générer et d'analyser des traces d'exécution de programmes Linux. Nous montrerons qu'avec une architecture simple couplée à un LLM performant, Pike permet de déboguer rapidement un crash, d'identifier un malware ou de fournir des analyses de haut niveau pertinentes, le tout via une interface de chat naturelle.

appledb_rs, un outil d'aide à la recherche sur plateformes Apple

25/09/2025
Développement
Outils
Au fil des années, la recherche sur les plateformes Apple s’est considérablement complexifiée, en grande partie à cause des nombreuses contre-mesures déployées au fil du temps par la marque à la pomme. Pour répondre à ce défi durant nos missions sur ces plateformes, nous avons développé appledb_rs: un outil open‑source (https://github.com/synacktiv/appledb_rs) qui extrait les données des fichiers IPSW (archive contenant le firmware Apple) et les organise de manière structurée, facilitant ainsi leur exploration et leur analyse.

Laravel: Analyse de fuite d'APP_KEY

10/07/2025
Outils
Pentest
En novembre 2024, Mickaël Benassouli et moi-même avons parlé des modèles de vulnérabilité basés sur le chiffrement Laravel lors de Grehack. Cependant, chacune de ces vulnérabilité nécessite l'accès à un secret : l'APP_KEY, nous avons souligné les risques de sécurité impliqués et mis en évidence que ce secret est souvent exposé dans les projets publics. L'histoire ne s'est pas arrêtée là, nous avons rassemblé un grand nombre d'APP_KEY et développé un nouvel outil pour identifier les modèles vulnérables à partir d'un ensemble d'ap...

Diving into ADB protocol internals (2/2)

16/12/2024
Développement
Outils
Our previous article laid the groundwork for understanding the ADB protocol and its usage scenarios. It primarily focused on the TCP/IP communication between the ADB Client and the ADB Server. However, this still required at this point an intermediate server to bridge our client and the Android device. In this article, we'll dive into the message protocol between ADB Server and adbd, with the goal of improving our Rust client library with capacity to fully interact with a device, eliminating the need for system dependency installatio...

Fuzzing confused dependencies with Depfuzzer

25/09/2024
Outils
In the landscape of software development, leveraging open-source libraries and packages through registries like NPM, PyPI, Go modules, and Crates for Rust has become standard practice. This approach facilitates the rapid integration of diverse functionalities into applications, driving both innovation and efficiency across the development community. While the benefits of using these resources are clear, the management of external dependencies introduces a set of considerations regarding security and maintainability. Inspired by Alex ...

Diving into ADB protocol internals (1/2)

12/09/2024
Développement
Outils
For those having experience working on Android devices, you may already be familiar with a useful tool called adb. This tool is invaluable for debugging, offering a unified way to execute shell commands, transfer files, install APKs, and much more. In this first blogpost, we will explore its underlying protocol between client and server and introduce a Rust crate called adb_client implementing it.

Battle of the parsers: PEG vs combinators

25/07/2024
Développement
Outils
Système
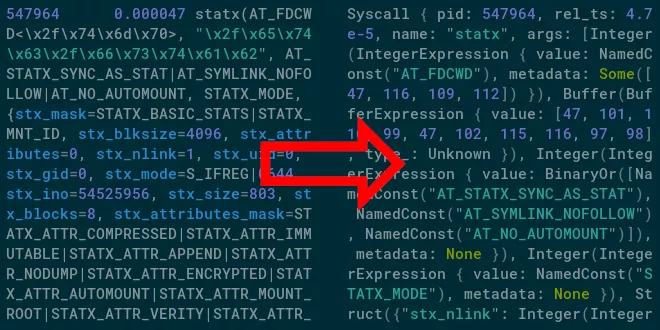
In this article we will compare two parsing strategies : PEG based and combinators based, from a developer's perspective, to parse Strace output for the SHH (Systemd Hardening Helper) Rust project.

👻 Souls without bodies, phantom types shenanigans 👻

26/04/2024
Outils
In this article, we will present strange data types that only exist in the realm of types, called phantom types. We will also briefly introduce GADTs, and how to emulate some of their safety guarantees in languages where they are not available. This simple technique can go a long way towards making APIs safer and more expressive.